Executive Outcome 11 — Prove it on demand

Evidence Readiness Sprint™

If an insurer, regulator, customer, auditor, or board asked us to prove this tomorrow, how quickly could we?

Assertions are cheap. Evidence is not. We test whether your important security and governance claims can actually be substantiated — and how long it takes to produce credible proof.

Test our evidence
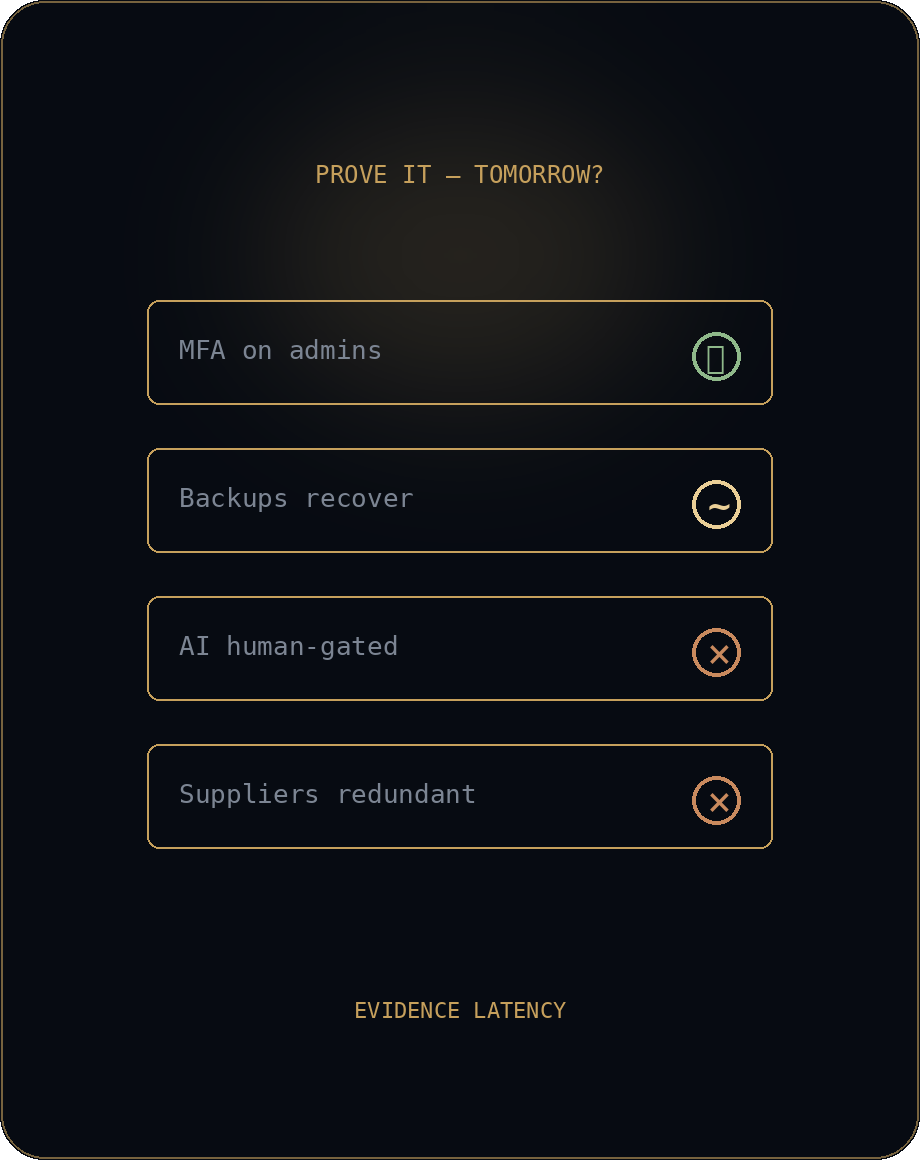
Control assertions and their evidence latency
Why this becomes a business problem

“MFA protects privileged accounts.” “Critical backups are recoverable.” “AI decisions require human approval above threshold X.” Every organization asserts these. Fewer can prove them on demand.

The time to produce credible evidence for a material assertion — its Evidence Latency — is the gap between what you claim and what you can defend. At claim time or under examination, that gap is the exposure.

What leadership needs to decide
The decision

Which assertions are immediately substantiated, which require investigation, and which cannot be proven — and what to fix before someone asks.

What Cyber Unveil does

List the assertions

The material control and governance claims your organization relies on — to insurers, regulators, customers, and the board.

Demand the proof

For each, we ask: prove it. Immediately, with investigation, partially, or not at all.

Measure evidence latency

How long it takes to produce credible evidence for each assertion — the real readiness gap.

Close the gaps

A prioritized plan to make the most consequential assertions provable before they are challenged.

The outcome

You can prove what you claim — before someone asks.

Leadership knows which of its material assertions can be substantiated immediately, which need work, and which cannot be proven at all — with a plan to close the gaps. Attestation gives way to demonstration.

What we measure
What you keep
Executive evidence
Evidence Readiness Statement™

A statement of which material assertions can be substantiated, how quickly, and which cannot — the readiness record an insurer, auditor, or board will test.

Who this is for
CISO — can we prove our controls?General Counsel — what is defensible?CFO — will the policy pay?Board — are we audit-ready?
Common triggers
Audit / regulator approachingInsurance renewalCustomer security reviewPost-incident evidence demandBoard assurance request
Bring us the decision

Prove it. Tomorrow.

If a cyber, technology, resilience, or AI decision carries material business consequence, bring us the decision before it becomes the loss.

Test our evidence

30 minutes · Independent · Vendor-neutral · Nothing sold